Responding to AI-Era Security Threats with AI-MiWork Guard
Reading a security advisory is not the same as completing the response.
MiWork Guard finds what needs attention, prioritizes the work, and revalidates the result. AI organizes the evidence and risks; administrators decide how to respond. The process becomes a trustworthy record.12
An illustration of the product's purpose, not an actual screen. Click any image in the article to view the original.
Why it matters now
AI can increase the speed and scale at which attackers find and exploit weaknesses. Preparing for new threats must go hand in hand with basic work to reduce known risks.3
Recent incidents leave a familiar task:
- On October 12, 2026, GitLab released important security fixes and urged affected users to update promptly.4
- The investigation into LiteLLM's compromised October 21 release described a previously exposed administrative key that had not been revoked.5
When a vulnerability has an effective fix, applying the security update in time can close the corresponding attack path. Other issues require actions beyond updating software. NIST's description of patching as preventive maintenance includes applying the relevant fixes and verifying the result.6
The practical challenge comes next. Purchased products, open-source programs, and libraries publish notices and updates on different schedules. Keeping track of what affects the company, who addressed it, and what remains is not easy.
Turn findings into prioritized work
MiWork Guard compares software and components observed on servers with security information. The report answers three practical questions:17
- Where is the affected software? Its location and current version.
- What should change first? Target versions and work priorities.
- Can it be fixed now? Fix availability and items whose actual use needs confirmation.
AI reviews collected evidence and organizes risks that deserve further attention. It supports the administrator's judgment rather than making arbitrary changes to the server.1
Turn a long list of warnings into work someone can carry out. Action plans and task lists can be saved as reports or spreadsheet-compatible files and shared with the person responsible.7
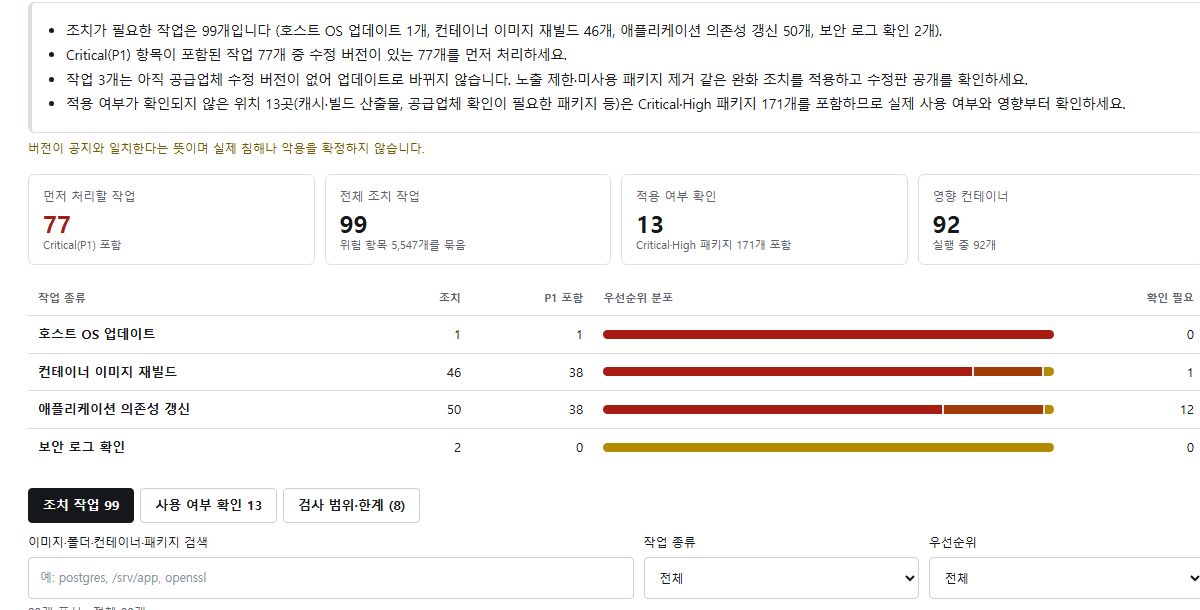
Actual action-plan screen. Internal identifying information is excluded.
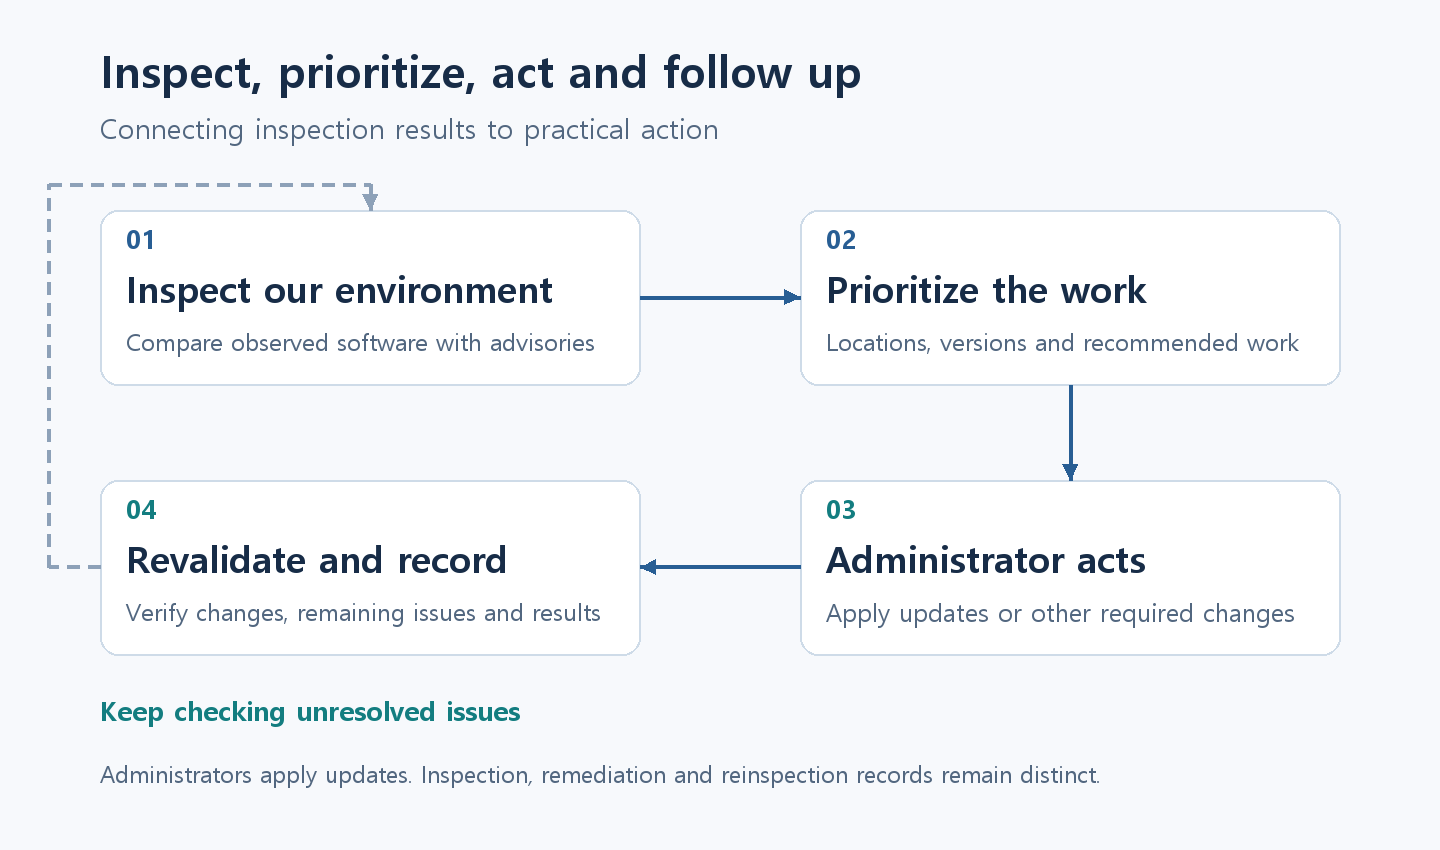
Revalidate the result and keep the record
A completed inspection is not a completed update. After the administrator performs remediation, another Guard inspection checks whether the change took effect and whether the previously observed issue remains.172
Connecting the initial findings, response records, and revalidation results shows what was found, how it was addressed, and what changed afterward. Trust comes not simply from keeping a record, but from checking the remediation result again.2
Tamper prevention protects those records. Remaining issues and uninspected areas stay visible, informing the next inspection or handover. This is not a guarantee of safety beyond the inspected scope.12
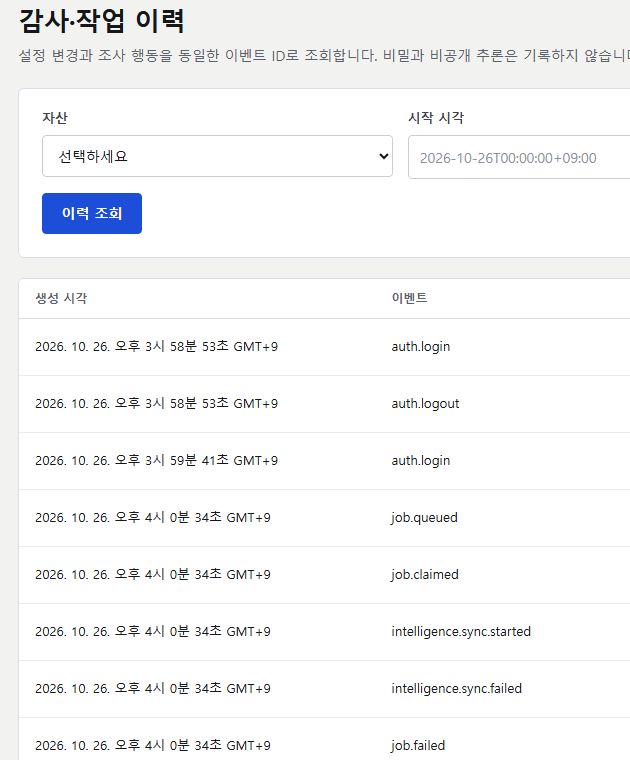
An excerpt from the actual activity history. Internal identifying information is excluded.
The current scope is Linux servers and running Docker containers. Administrators perform the actual updates; areas that could not be fully checked are marked partial or uninspected.17
The gap is often not a lack of security knowledge, but the amount of work to keep in view. Reducing that gap and following through with action and revalidation is why MiWork Guard is needed.
References
Footnotes
Subscribe to new posts
Follow new posts through the RSS or Atom feed.
Reactions and comments
Sign in with GitHub to comment and leave a reaction (like). Comments and GitHub usernames are public; editing, deletion, and reporting are handled through GitHub Discussions.